
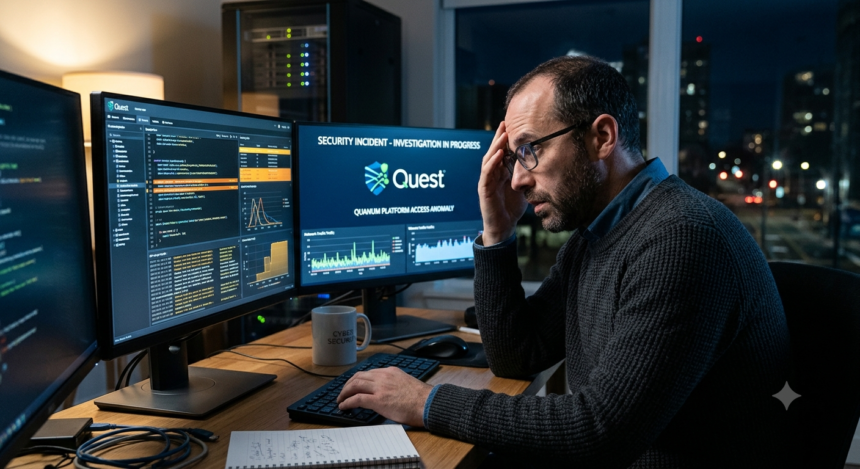
Quest Diagnostics has disclosed unauthorized access to patient information through its Quanum platform, highlighting growing cybersecurity risks for healthcare organizations and medical technology providers.
Medical data security has become an increasingly urgent concern as healthcare providers rely on digital platforms to manage patient records, diagnostic testing, and billing operations. The latest incident involves Quest Diagnostics, a major U.S. laboratory testing company that has confirmed a cyberattack affecting sensitive information stored within one of its systems.
According to a regulatory filing dated October 23, 2026, the company discovered an attack targeting Quanum, a platform used by healthcare professionals to order laboratory tests and manage related administrative activities. Quest confirmed that unauthorized access involved certain patient records, although the full scope of the incident remains under investigation.
Quanum Platform at the Center of the Incident
Quanum supports communication and workflows between medical laboratories, hospitals, doctors’ offices, and other healthcare organizations. Its capabilities include laboratory test requests and billing processes, making it an important component of the healthcare information ecosystem.
- Advertisement -
Because these systems handle sensitive medical and administrative information, unauthorized access can create significant privacy concerns for patients and healthcare providers.
In its security notice, Quest stated that protected health information belonging to some patients had been taken. The company identified personal information and patient records among the affected data but has not yet provided a complete breakdown of the information compromised.
Quest has notified law enforcement and launched an investigation into the incident. However, several important questions remain unanswered, including when the intrusion began, how many individuals were affected, and whether the attackers attempted to demand a ransom.
The Scale of the Breach Remains Unclear
One of the biggest concerns is the potential reach of the compromised platform. Quest’s published materials indicate that Quanum serves approximately 500,000 clinicians across thousands of locations in North America.
However, the number of healthcare professionals using a platform does not establish how many patient records were exposed. Until the investigation progresses, the total number of affected patients and healthcare organizations remains unknown.
- Advertisement -
For individuals whose information was accessed, the potential consequences may extend beyond the immediate exposure of medical records. Personal information can be exploited for identity fraud, targeted phishing campaigns, and other forms of cybercrime.
Healthcare organizations may also face operational disruption, regulatory scrutiny, and reputational damage when sensitive patient information is compromised.
Healthcare Cyberattacks Continue to Create Disruption
The Quest incident adds to a series of cybersecurity events affecting the healthcare sector in 2026. Other reported incidents have involved medical technology manufacturer Stryker, medical device company Boston Scientific, healthcare technology provider CareCloud, Craneware, and pharmaceutical distribution giant McKesson.
- Advertisement -
These incidents demonstrate that cyber risks extend throughout the healthcare supply chain, affecting not only hospitals and laboratories but also technology vendors and companies responsible for managing medical information.
Healthcare organizations are particularly attractive targets because their systems contain valuable personal and medical data. Criminal groups may attempt to steal this information and use the threat of public disclosure to pressure organizations into paying a ransom.
Quest also experienced a significant data breach in 2019, when a cyberattack involving a third-party billing company exposed information associated with approximately 11.9 million patient records.
What Healthcare Organizations Can Learn
The incident reinforces the importance of protecting patient information across every system involved in healthcare delivery.
Organizations should regularly review access permissions, strengthen authentication procedures, monitor systems for suspicious activity, and maintain effective incident response plans. Third-party vendors must also be included in cybersecurity assessments because weaknesses in connected systems can introduce additional risks.
Clear communication is equally important when a breach occurs. Timely notifications, transparent updates, and practical guidance can help affected individuals understand the situation and take appropriate precautions.
Conclusion
The Quest Diagnostics incident highlights the growing challenges of safeguarding sensitive information in an increasingly connected healthcare environment. Although the number of affected patients and the full extent of the compromised data have not yet been established, the confirmed exposure of patient information underscores the importance of stronger cybersecurity controls.
As investigations continue, healthcare providers and technology companies will need to prioritize data protection, vendor oversight, and rapid incident response to maintain patient trust and reduce the risks associated with future attacks.