By using this site, you agree to the Privacy Policy.
Accept
Content LeadContent Lead
  • Home
  • Latest News
  • Technology
  • Business
  • Marketing
  • White Paper
  • Event
  • Contact Us
Reading: The AI Graveyard Is Growing: What Failed AI Products Can Teach the Industry
Share
Aa
Content LeadContent Lead
Aa
Search
  • Home
  • Latest News
  • Technology
  • Business
  • Marketing
  • White Paper
  • Event
  • Contact Us
Follow US
© 2024 - All Right Reserved by Content Lead
- Advertisement -
Home » Blog » The AI Graveyard Is Growing: What Failed AI Products Can Teach the Industry
Latest NewsTechnology

The AI Graveyard Is Growing: What Failed AI Products Can Teach the Industry

Sunil Pachori
Sunil Pachori
Share
6 Min Read
The AI Graveyard Is Growing What Failed AI Products Can Teach the Industry

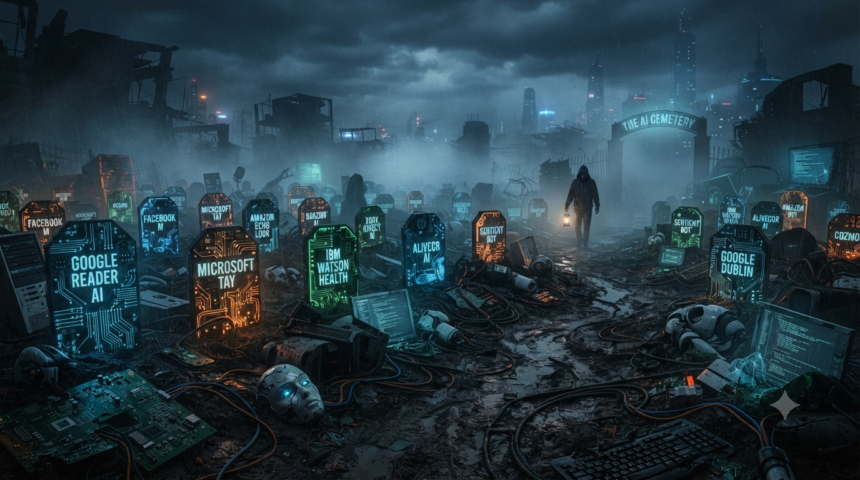
Artificial intelligence is attracting enormous investment, launching new startups almost every week, and reshaping products across the technology industry. But behind the success stories sits another rapidly growing category: AI products that didn’t survive.

Contents
Relay Shows the Risk of Competing With PlatformsEven OpenAI Has Had MisstepsApple’s Siri AI Became a Lesson in OverpromisingMicrosoft’s Recall Triggered Privacy ConcernsAI Hardware Had Its Own Reality CheckSmaller AI Products Are Feeling the Platform SqueezeFailure Is Becoming Part of the AI Experiment

Some were promising startups that ran out of room to compete. Others were ambitious features from technology giants that faced privacy concerns, technical problems, poor adoption, or user backlash.

The growing “AI graveyard” offers an important reminder: adding AI to a product doesn’t automatically create a sustainable business.

Relay Shows the Risk of Competing With Platforms

AI workflow automation startup Relay is one of the latest examples.

- Advertisement -

Designed as an AI-powered alternative to automation platforms such as Zapier, Relay allowed users to automate email and task workflows through AI agents.

But the competitive landscape changed quickly.

As companies such as OpenAI and Google started incorporating similar agentic automation capabilities directly into their platforms, maintaining a differentiated standalone product became increasingly difficult. Relay eventually shut down after five years.

Its story reflects a wider challenge for AI startups: today’s innovative standalone feature can become tomorrow’s built-in platform capability.

Even OpenAI Has Had Missteps

Large AI companies aren’t immune either.

- Advertisement -

OpenAI attempted to redesign ChatGPT into a broader “super app,” combining experiences such as Chat, Codex, and Work while renaming the familiar interface ChatGPT Classic.

Users criticized the redesigned experience as confusing, and OpenAI subsequently restored the more familiar interface.

The company has also consolidated products into ChatGPT.

- Advertisement -

Its standalone AI browser, ChatGPT Atlas, was discontinued, while capabilities from Operator, an AI agent designed to perform web tasks, were integrated into the broader ChatGPT experience.

OpenAI’s Sora video-sharing platform faced another problem: expensive operations combined with challenges retaining users. It shut down in March 2026.

Apple’s Siri AI Became a Lesson in Overpromising

Apple’s AI journey produced a different kind of setback.

When Apple Intelligence was announced in 2024, a dramatically smarter Siri was one of its biggest promises. Apple presented a future assistant capable of understanding personal context, working across applications, and completing more sophisticated tasks.

But technical and engineering challenges repeatedly delayed the upgraded Siri.

The new AI-powered version eventually arrived through the iOS 27 rollout, but its difficult journey demonstrated the risks of marketing advanced AI capabilities before they’re ready for consumers.

Microsoft’s Recall Triggered Privacy Concerns

Microsoft faced another fundamental AI challenge: trust.

Its Recall feature was designed to periodically capture activity on Windows PCs, effectively giving users a searchable history of what they’d previously viewed.

The concept immediately generated security and privacy concerns because such a database could potentially contain sensitive information.

Microsoft delayed Recall for nearly a year while reworking its protections, but security questions have continued even after its redesign.

AI Hardware Had Its Own Reality Check

Few AI hardware products attracted as much attention as the Humane AI Pin.

Humane raised $230 million and envisioned a wearable AI device capable of reducing dependence on smartphones.

Reality was considerably tougher.

Performance problems hurt the product, and customers were eventually warned about a potential battery fire risk involving its charging case. Humane shut down the AI Pin business in February 2025, with HP acquiring most of its assets for $116 million.

The Rabbit R1 faced similar early criticism.

Although Rabbit reported selling 100,000 units shortly after launch, reviewers described the initial product as unfinished and unreliable. Unlike Humane, however, Rabbit continues developing the R1 and expanding its agentic capabilities.

Smaller AI Products Are Feeling the Platform Squeeze

Other casualties reveal how difficult competing against established platforms can be.

Huxe, created by former NotebookLM developers, transformed written information into conversational audio but shut down as larger platforms introduced comparable AI experiences.

Yupp, which allowed people to compare hundreds of AI models, closed after failing to establish sufficient product-market fit.

Meanwhile, Figgs AI attracted more than one million users with customizable AI characters, but operating the free service became too expensive to sustain.

Failure Is Becoming Part of the AI Experiment

The important lesson from the AI graveyard isn’t that artificial intelligence is failing.

It’s that AI alone isn’t a business model.

Research cited in the source says roughly 42% of corporate AI initiatives are eventually abandoned, with factors including funding limitations, technical difficulties, competition, scaling problems, and insufficient demand.

As the AI market matures, survival will depend on more than impressive models and viral launches.

Products will need clear differentiation, sustainable economics, genuine user demand, strong security, and enough value to survive when the biggest technology platforms inevitably build competing features.

The AI boom will create winners — but its growing graveyard may teach the industry just as much.
You Might Also Like

ClickFix Attacks Are Tricking Mac and Windows Users Into Infecting Their Own Computers

Scammers Target Hundreds of Thousands of Crypto Users After Trezor Vendor Breach

Instagram Hands Your Grid Over to Photos You Didn’t Post

Apple’s First Fold Costs $1,999. The Watch Now Listens

Cook Hands Ternus a $5 Trillion Company and Four Problems

TAGGED: AI Graveyard, AI Hardware, AI Startups, artificial intelligence, Big Tech, Product Failure, Tech Industry
Sunil Pachori September 15, 2026 September 15, 2026
Share This Article
Facebook Twitter Whatsapp Whatsapp LinkedIn
Previous Article ClickFix Attacks Are Tricking Mac and Windows Users Into Infecting Their Own Computers Cybercriminals are increasingly using a surprisingly simple technique to compromise computers convincing victims to execute the malicious code themselves. Known as ClickFix, the attack method is emerging as a significant cybersecurity threat affecting both Windows and macOS users. Instead of relying entirely on software vulnerabilities or secretly installing malware, attackers use social engineering to persuade users to copy and execute commands directly on their computers. A recent campaign involving fake HBO Max advertisements on Reddit demonstrates how convincing these attacks can become when criminals gain access to trusted accounts. What Is a ClickFix Attack A typical ClickFix attack begins when someone visits a malicious website or a legitimate website that has been compromised. The page may display what appears to be a normal CAPTCHA, verification request or anti-bot security check. The user is told that an additional step is required before they can continue. Instead of simply clicking a checkbox, however, the website provides instructions asking the visitor to copy a command and paste it into Windows Command Prompt or PowerShell, or Terminal on macOS. That should immediately be considered a major warning sign. Once the command is executed, it can download and install information-stealing malware on the device. The malware may then attempt to collect sensitive information including saved passwords, browser sessions, authentication data and cryptocurrency wallet information. What makes ClickFix particularly dangerous is that the victim performs the critical execution step. Because command-line tools provide direct access to operating-system functions, malicious activity initiated this way can sometimes bypass or complicate traditional security defenses. HBO Max Reddit Account Used in Malicious Campaign One of the latest ClickFix incidents involved advertisements appearing to originate from an official HBO Max account on Reddit. Security researchers found advertisements directing users toward websites designed to resemble legitimate HBO Max pages. The sites then presented visitors with ClickFix-style instructions intended to convince them to execute malicious commands. The situation was particularly concerning because attackers were not simply impersonating HBO Max with a newly created profile. Reddit confirmed that an HBO Max account authorized to run advertising on the platform had been compromised and subsequently used to distribute advertisements containing malicious links. Reddit said it locked the affected account and removed the advertisements after discovering the incident. The total scale of the campaign remains unclear. Reddit did not disclose how many people saw or interacted with the malicious advertisements, and it is not known how many computers may have ultimately been infected. Why ClickFix Is So Effective ClickFix demonstrates an important shift in modern cybercrime. Instead of breaking through a computer's defenses directly, attackers manipulate users into performing actions that would normally require malware or an exploit. CAPTCHAs and verification screens are now common parts of browsing the internet, which makes a fake security check appear familiar and potentially trustworthy. The use of legitimate or previously trusted accounts makes the attack even more convincing. Cybercriminals are essentially combining malvertising, account compromise, phishing and social engineering into a single attack chain. How Users Can Protect Themselves The most important rule is simple never paste an unfamiliar command into Terminal, PowerShell or Command Prompt because a website tells you to. Legitimate CAPTCHA systems do not normally require users to open operating-system command-line tools and execute copied code. Users should also remain cautious even when an advertisement appears to come from a verified or recognizable brand. A legitimate account can itself be compromised. Organizations managing Windows environments can consider restricting command-line access where employees do not need it. Security researcher Kevin Beaumont has noted that organizations can apply controls across managed Windows environments to reduce opportunities for this type of exploitation. Mac users can also consider security tools designed to detect persistent software installations and suspicious system changes. The Bigger Cybersecurity Lesson ClickFix attacks highlight a fundamental challenge for cybersecurity sophisticated malware isn't always necessary when attackers can convince people to execute malicious instructions themselves. As criminals increasingly combine trusted brands, compromised accounts, convincing websites and familiar verification interfaces, users need to evaluate not only what they click, but also what a website asks them to do afterward. If a website suddenly asks you to open Terminal, PowerShell or Command Prompt and paste a command, stop. That “verification” could actually be asking you to hack your own computer. ClickFix Attacks Are Tricking Mac and Windows Users Into Infecting Their Own Computers
Leave a comment

Leave a Reply

Your email address will not be published. Required fields are marked *

Latest News

ClickFix Attacks Are Tricking Mac and Windows Users Into Infecting Their Own Computers Cybercriminals are increasingly using a surprisingly simple technique to compromise computers convincing victims to execute the malicious code themselves. Known as ClickFix, the attack method is emerging as a significant cybersecurity threat affecting both Windows and macOS users. Instead of relying entirely on software vulnerabilities or secretly installing malware, attackers use social engineering to persuade users to copy and execute commands directly on their computers. A recent campaign involving fake HBO Max advertisements on Reddit demonstrates how convincing these attacks can become when criminals gain access to trusted accounts. What Is a ClickFix Attack A typical ClickFix attack begins when someone visits a malicious website or a legitimate website that has been compromised. The page may display what appears to be a normal CAPTCHA, verification request or anti-bot security check. The user is told that an additional step is required before they can continue. Instead of simply clicking a checkbox, however, the website provides instructions asking the visitor to copy a command and paste it into Windows Command Prompt or PowerShell, or Terminal on macOS. That should immediately be considered a major warning sign. Once the command is executed, it can download and install information-stealing malware on the device. The malware may then attempt to collect sensitive information including saved passwords, browser sessions, authentication data and cryptocurrency wallet information. What makes ClickFix particularly dangerous is that the victim performs the critical execution step. Because command-line tools provide direct access to operating-system functions, malicious activity initiated this way can sometimes bypass or complicate traditional security defenses. HBO Max Reddit Account Used in Malicious Campaign One of the latest ClickFix incidents involved advertisements appearing to originate from an official HBO Max account on Reddit. Security researchers found advertisements directing users toward websites designed to resemble legitimate HBO Max pages. The sites then presented visitors with ClickFix-style instructions intended to convince them to execute malicious commands. The situation was particularly concerning because attackers were not simply impersonating HBO Max with a newly created profile. Reddit confirmed that an HBO Max account authorized to run advertising on the platform had been compromised and subsequently used to distribute advertisements containing malicious links. Reddit said it locked the affected account and removed the advertisements after discovering the incident. The total scale of the campaign remains unclear. Reddit did not disclose how many people saw or interacted with the malicious advertisements, and it is not known how many computers may have ultimately been infected. Why ClickFix Is So Effective ClickFix demonstrates an important shift in modern cybercrime. Instead of breaking through a computer's defenses directly, attackers manipulate users into performing actions that would normally require malware or an exploit. CAPTCHAs and verification screens are now common parts of browsing the internet, which makes a fake security check appear familiar and potentially trustworthy. The use of legitimate or previously trusted accounts makes the attack even more convincing. Cybercriminals are essentially combining malvertising, account compromise, phishing and social engineering into a single attack chain. How Users Can Protect Themselves The most important rule is simple never paste an unfamiliar command into Terminal, PowerShell or Command Prompt because a website tells you to. Legitimate CAPTCHA systems do not normally require users to open operating-system command-line tools and execute copied code. Users should also remain cautious even when an advertisement appears to come from a verified or recognizable brand. A legitimate account can itself be compromised. Organizations managing Windows environments can consider restricting command-line access where employees do not need it. Security researcher Kevin Beaumont has noted that organizations can apply controls across managed Windows environments to reduce opportunities for this type of exploitation. Mac users can also consider security tools designed to detect persistent software installations and suspicious system changes. The Bigger Cybersecurity Lesson ClickFix attacks highlight a fundamental challenge for cybersecurity sophisticated malware isn't always necessary when attackers can convince people to execute malicious instructions themselves. As criminals increasingly combine trusted brands, compromised accounts, convincing websites and familiar verification interfaces, users need to evaluate not only what they click, but also what a website asks them to do afterward. If a website suddenly asks you to open Terminal, PowerShell or Command Prompt and paste a command, stop. That “verification” could actually be asking you to hack your own computer.
ClickFix Attacks Are Tricking Mac and Windows Users Into Infecting Their Own Computers
Latest News Security September 14, 2026
Scammers Target Hundreds of Thousands of Crypto Users After Trezor Vendor Breach
Latest News Security September 11, 2026
Instagram Hands Your Grid Over to Photos You Didn't Post
Instagram Hands Your Grid Over to Photos You Didn’t Post
Applications Latest News September 10, 2026
Apple’s First Fold Costs $1,999. The Watch Now Listens
Latest News Technology September 9, 2026
Content-Lead is a vibrant community that brings together professionals passionate about marketing strategy and the latest in marketing technology. With over 1 million members, it has rapidly become a key player in helping businesses navigate the complex world of modern marketing. By focusing on both strategy and technological innovation, Content-Lead equips its members with the tools and insights needed to drive impactful advertising campaigns.
Facebook X-twitter Linkedin

Quick Link

Menu
  • Home
  • Latest News
  • Technology
  • Business
  • Marketing
  • White Paper
  • Event
  • Contact Us

About US

Menu
  • Privacy Policy
  • GDPR Policy
  • Terms of Use

Subscribe to Our Newsletter

© 2026 – All Right Reserved by Content Lead.